Linux.Wifatch
Linux.Wifatchは、オープンソースのマルウェアである。悪意のある行為には使用されず、他のマルウェアからデバイスを保護することを目的としていると指摘されている[2]。
| 別名 | |
|---|---|
| 作者 | The White Team |
| 標的OS | Linux |
| 言語 | Perl[2] |
概要
Linux.Wifatchはアンチウイルスソフトウェアのように動作し、Peer to Peerを介して定義を更新し、システム内にある他のマルウェアを削除する[3]。
Linux.Wifatchは、少なくとも2014年11月から活動している[4]。このマルウェアの作者は、Linux.Wifatchのアイデアは、Cornaボットネットの論文を読んだ後に生まれたと述べている[5]。Linux.Wifatchは2015年10月5日に作者によって、GNU General Public Licenseの下でGitLabで公開された[6]。
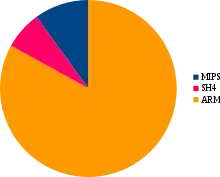
動作
Linux.Wifatchの主な感染経路は、弱い認証情報やデフォルトのtelnet認証情報を使ってデバイスにログインすることである[2][4]。
感染すると、Linux.Wifatchは他のマルウェアを削除し、telnetアクセスを無効にして、"Telnet has been closed to avoid further infection of this device. Please disable telnet, change telnet passwords, and/or update the firmware."(このデバイスへのさらなる感染を避けるため、telnetは閉じられました。Telnetを無効にするか、Telnetのパスワードを変更するか、ファームウェアを更新してください。)というメッセージを表示する[2]。
脚注
- Schick, Shane (2015年10月6日). “Linux.Wifatch: The Router Virus That May Be Secretly Defending You From Other Malware”. Security Intelligence. 2016年12月7日時点のオリジナルよりアーカイブ。2016年12月7日閲覧。
- Ballano, Mario (2015年10月1日). “Is there an Internet-of-Things vigilante out there?”. Symantec. 2016年11月14日閲覧。
- Das, Samburaj (2015年10月2日). “Linux.Wifatch: Vigilante Hacker Infects Routers with Malware to Fight Bad Malware”. hacked.com. 2016年11月14日閲覧。
- Kovacs, Eduard (2015年10月7日). “Developers of Mysterious Wifatch Malware Come Forward”. securityweek.com. 2016年11月15日閲覧。
- “linux.wifatch”. The White Team (2015年10月5日). 2016年11月15日閲覧。
- Cimpanu, Catalin (2015年10月7日). “Creators of the Benevolent Linux.Wifatch Malware Reveal Themselves”. Softpedia. 2016年11月14日閲覧。
外部リンク
This article is issued from Wikipedia. The text is licensed under Creative Commons - Attribution - Sharealike. Additional terms may apply for the media files.