MD4
MD4は、1990年にマサチューセッツ工科大学のロナルド・リベストによって開発されたハッシュ関数の一種。暗号ハッシュ関数を実装する。SHA・RIPEMDなどに影響を及ぼした。
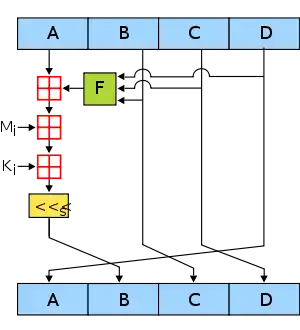
One MD4 operation : MD4 consists of 48 of these operations, grouped in three rounds of 16 operations. F is a nonlinear function; one function is used in each round. Mi denotes a 32-bit block of the message input, and Ki denotes a 32-bit constant, different for each operation.
| 一般 | |
|---|---|
| 設計者 | ロナルド・リベスト |
| 初版発行日 | 1990年10月[1] |
| シリーズ | MD2, MD4, MD5, MD6 |
| 詳細 | |
| ダイジェスト長 | 128ビット |
| ラウンド数 | 3 |
| 最良の暗号解読法 | |
| ハッシュ計算2回でハッシュ衝突を作成可能[2] | |
与えられた入力に対して、128ビットのハッシュ値を出力する。
MD4に対する脆弱性は1991年に実証された。2004年には、MD4におけるハッシュ衝突を作成することが可能であることが報告された。
脚注
- “The MD4 Message Digest Algorithm”. Network Working Group (1990年10月). 2011年4月29日閲覧。
- Yu Sasaki, et al. (2007). New message difference for MD4.
外部リンク
- RFC 1320
- Collisions for Hash Functions MD4, MD5, HAVAL-128 and RIPEMD MD4その他においてハッシュ衝突を作成することが可能であることを主張している論文。
- MD2, MD4, MD5 Online Calculator Calculate file hashes using an on-line web form.
| |||||||||||||||||||||||||||||
 カテゴリ | |||||||||||||||||||||||||||||
This article is issued from Wikipedia. The text is licensed under Creative Commons - Attribution - Sharealike. Additional terms may apply for the media files.